Updated: These vulnerabilities have been fixed in versions 8.5.12, 8.4.27, 8.3.36 and 8.2.35.
First of all, check your current PHP and PHP-FPM versions:
php -v

# If you have php-fpm installed
# Replace 8.3 with your version
php-fpm8.3 -v
Check whether your current version falls into the affected branches:
Affected versions:
- 8.2 branch: version 8.2.34 and lower
- 8.3 branch: version 8.3.35 and lower
- 8.4 branch: version 8.4.26 and lower
- 8.5 branch: version 8.5.11 and lower
As of October 21, 2026, there is no official update available to fix these vulnerabilities.
These vulnerabilities have now been fixed in versions 8.5.12, 8.4.27, 8.3.36 and 8.2.35.
If for some reason you can't update to these versions, you can still reduce your exposure by turning off session upload progress.
To do this, open your PHP configuration file (php.ini).
It's typically located at /etc/php/*/fpm/php.ini:
sudo nano /etc/php/8.3/fpm/php.ini
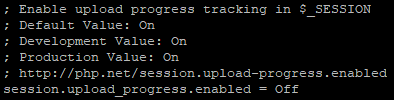
Find the session.upload_progress.enabled parameter and set it to Off:
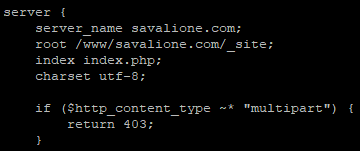
Additionally, if you use a reverse proxy such as nginx, it's a good idea to block requests that could exploit this vulnerability. Add the following rule to your site configuration:
if ($http_content_type ~* "multipart") {
    return 403;
}
It should look something like this:
Once the official security patches are released, make sure to update PHP and PHP-FPM immediately.